
HOC Shorts |
Apple issued emergency software updates across its lineup—including iOS 27.2.1, iPadOS 27.2.1, macOS Golden Gate 27.2.1, visionOS 27.2.1, and watchOS 27.2.1—targeting serious privacy vulnerabilities.
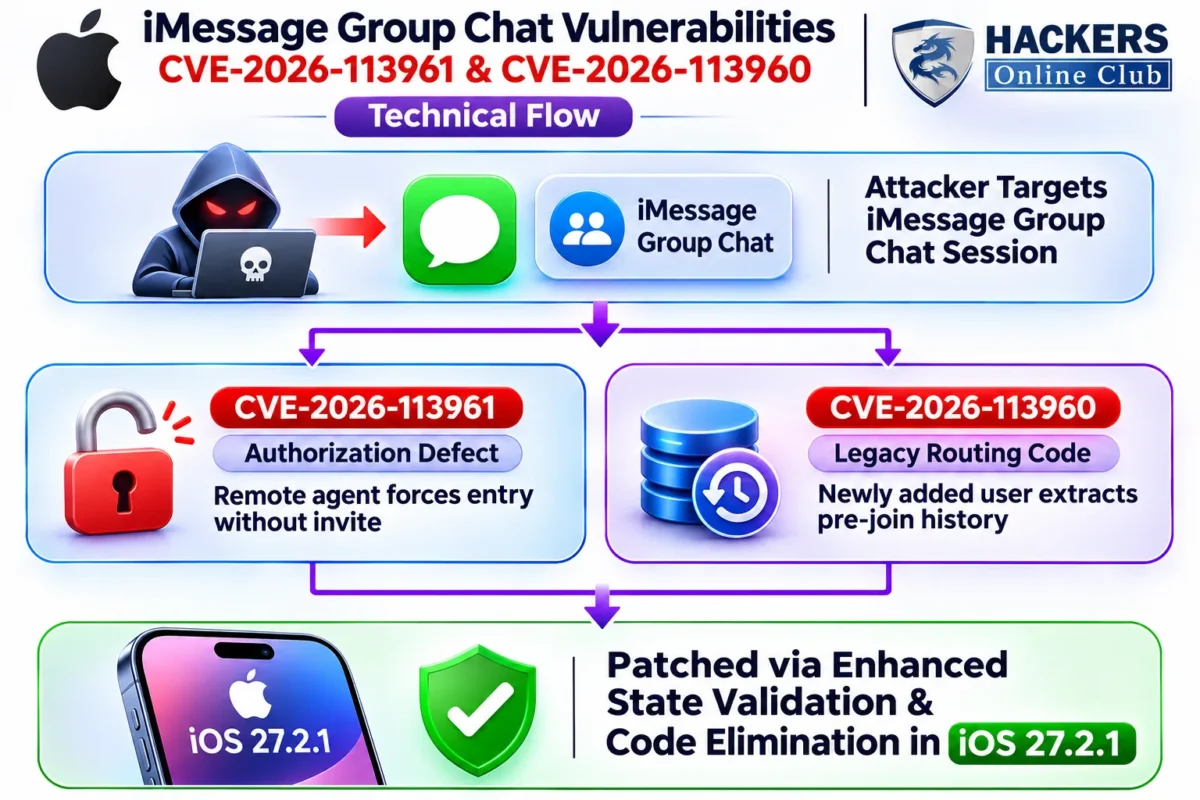
- The Silent Join Bug (`CVE-2026-113961`): An authorization logic error allowed a remote attacker to silently join iMessage group chats without an invitation or victim interaction, enabling unauthorized access to live group messages.
- Pre-Join Message Leakage (`CVE-2026-113960`): A secondary flaw allowed newly added participants to view historical group messages sent prior to their arrival.
- Immediate Action Required: Apple addressed the authorization logic with state-management validation and removed the legacy routing code. Users must update immediately to secure their group messaging infrastructure.
Apple Fixes Critical iMessage Flaws Exposing Group Conversations
Apple fixes emergency security updates across its entire software ecosystem, addressing high-severity privacy flaws that compromised the integrity of end-to-end encrypted iMessage group chats.
Disclosed alongside broader wireless vulnerabilities, the iMessage bugs allowed remote actors to manipulate group state configurations, enabling eavesdropping without physical access or user interaction.
Technical Breakdown of the iMessage Vulnerabilities
The security disclosures highlight two distinct breakdowns in Apple’s group chat state management:
1. Remote Uninvited Join (`CVE-2026-113961`)
The Mechanism: An authorization logic error in the messaging daemon allowed an unauthenticated remote entity to inject registration keys into an active group thread without receiving an invitation from an existing member.
The Threat Vector: Because the injection occurred at the protocol layer, the attacker could join group threads silently, intercepting incoming encrypted messages without alerting active participants.
2. Historical Message Leakage (`CVE-2026-113960`)
- The Mechanism: The iMessage key distribution logic contained legacy routing code that failed to properly segment chat histories when new participants joined.
- The Threat Vector: Upon joining an existing group, a user could trigger a state re-sync that exposed historical messages transmitted prior to their invitation.
Platform Patch Matrix
Apple backported and pushed these updates across all active product branches:
| Platform | Fixed OS Version | Remediation Method |
| iPhone & iPad | iOS / iPadOS 27.2.1 (and 26.7.3) | Improved state-management validation & code removal |
| Mac Desktop & Laptops | macOS Golden Gate 27.2.1 (and Tahoe 26.7.3) | System framework updates via System Settings |
| Apple Vision Pro | visionOS 27.2.1 | OTA system updates |
| Apple Watch | watchOS 27.2.1 | Security framework hotfix |
How to Verify and Update Immediate Defenses
Security administrators and end users must ensure their fleet devices are running updated binaries:
1. Trigger Manual Software Update: Navigate to `Settings > General > Software Update` on iOS/iPadOS devices and install iOS 27.2.1 immediately.
2. Audit Mac Workstations: Open `System Settings > General > Software Update` on macOS to apply corresponding core security updates.
3. Verify Fleet Management Policies: Enterprise MDM administrators should enforce a short grace period for compliance rules to mandate update deployment across remote mobile assets.