
HOC Shorts
The Federal Bureau of Investigation (FBI) removed an Accenture contractor from bureau assignments following a severe data breach.
- The Root Cause: The breach stemmed from a failure to apply a critical security patch on an Oracle PeopleSoft platform managing the FBI’s job portal (`FBIJobs.gov`).
- Threat Actor: Extortion syndicate ShinyHunters claimed responsibility, leveraging the unpatched PeopleSoft vulnerability to infiltrate the system.
- Impacted Data: Exfiltrated records include sensitive personnel details, counterintelligence assignment data, residential addresses of human intelligence (HUMINT) operatives, and employee medical and psychiatric records.
The Federal Bureau of Investigation (FBI) has removed an Accenture contractor from its IT infrastructure team following a data breach that exposed sensitive personal and operational information belonging to thousands of FBI employees.
According to Reuters, the contractor was removed after an internal review found that an important security update had not been applied to a third-party administrative system. The missed update left a security vulnerability that threat actors were able to exploit, creating an entry point into the system and contributing to the breach.
“To date, our review has determined that the incident occurred as the result of a security failure of a platform managed by a third-party organization — after a contractor failed to implement a security patch explicitly issued to secure the platform,” FBI cyber chief Brett Leatherman said in the statement to reuters. “As such, the FBI has removed the contractor and taken all necessary steps to both mitigate any further risk and protect our workforce.”
Technical Breakdown & Attack Vector
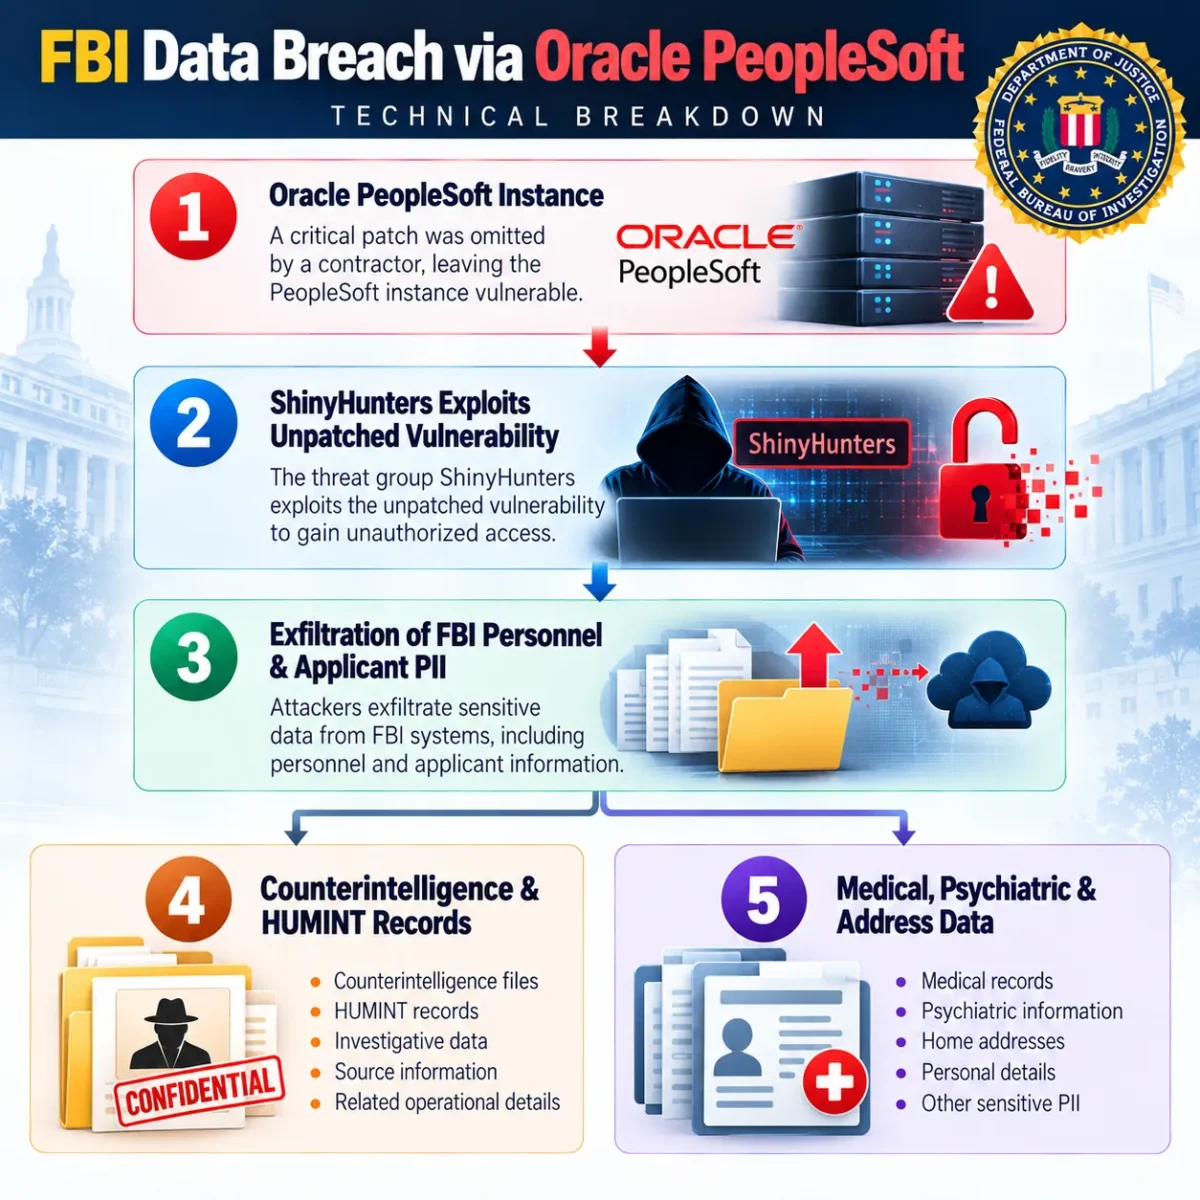
- Unpatched PeopleSoft Flaw: The breach targeted an instance of Oracle PeopleSoft running beneath the bureau’s career portal (`FBIJobs.gov`), managed externally by Accenture.
- Prior Industry Warnings: Google’s Threat Intelligence unit and Oracle had previously issued alerts regarding active exploitation campaigns against unpatched PeopleSoft applications. The contractor failed to apply the necessary Critical Patch Update (CPU) in a timely manner.
- Data Exfiltration: Threat actors extracted detailed records containing:
– Counterintelligence operational assignments and personnel histories.
– Physical addresses of active human intelligence (HUMINT) operatives.
– Confidential employee medical and psychiatric evaluations.
– Full applicant records and background check submissions.
Threat Actor Attribution & Response
The attack was claimed by ShinyHunters, a high-profile cybercrime syndicate known for large-scale data theft and extortion.
- Non-Monetary Demands: Uncharacteristically, the threat group stated the breach was executed out of retaliation rather than financial gain, demanding that the FBI officially retract a security advisory published in May detailing the group’s tactics, techniques, and procedures (TTPs).
- Law Enforcement Actions: Reports indicate law enforcement authorities in Jordan recently detained a key ShinyHunters suspect who is actively cooperating with international agencies to determine the full operational impact of the breach.
Incident Matrix
| Component | Status / Details |
| Primary Target | FBIJobs.gov / Oracle PeopleSoft Infrastructure |
| Responsible Third-Party | Accenture (Contractor personnel removed) |
| Threat Group | ShinyHunters |
| Root Cause | Omitted vendor security patch (PeopleSoft vulnerability) |
| Operational Impact | Severe blow to FBI HUMINT and counterintelligence operational security |