
Browsing Tag
SOC
12 posts
How Hackers Exploit AI agents Claude Code Enterprise Network Intrusions
HOC Shorts Adversaries are transitioning from using Large Language Models (LLMs) as passive reference tools to actively exploit…
50 SOC Analyst Interview Questions and Answers (2026 Guide)
By HOC Team | Last updated: August 30, 2026 | Read time: ~26 min 50 SOC Analyst Interview…
Best SIEM Tools For SOC Analysts: Splunk vs Sentinel vs QRadar (2026)
By HOC Team | Last updated: August 29, 2026 | Read time: ~25 min In 2026, the average…
Active Directory Security: Hardening Guide and Common Attack Paths (2026)
By HOC Team | Last updated: August 2026 | Read time: ~25 min When the NotPetya malware spread…
MITRE ATT&CK Framework Explained: How to Use It for Threat Detection (2026)
By HOC Team | Last updated: July 2026 | Read time: ~22 min In the months following the…
Splunk Tutorial for Beginners: Search, Dashboards and Alerts (2026)
By HOC Team | Last updated: July 2026 | Read time: ~25 min Splunk is the most widely…
What is SOAR? Security Orchestration, Automation and Response Explained (2026)
By HOC Team | Last updated: July 2026 | Read time: ~20 min A mid-sized financial services firm…
Threat Hunting Tutorial: How to Proactively Hunt Threats in Your Network (2026)
By HOC Team | Last updated: July 2026 | Read time: ~22 min In August 2022, Mandiant’s incident…
Incident Response Plan Template: Step-by-Step Guide for 2026
By HOC Team | Last updated: July 2026 | Read time: ~24 min At 2:17 AM on a…
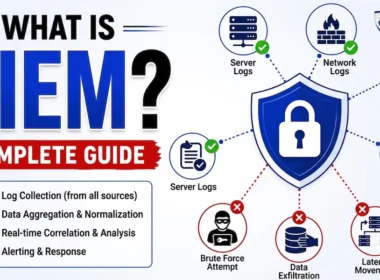
What is a SIEM? How it Works, Use Cases, and Top Tools (2026)
By HOC Team | Last updated: July 2026 | Read time: ~22 min On 14 December 2020, FireEye announced…