
HOC Shorts
PHP security updates on November 19, 2026, fixing 18 CVEs in total—including seven critical bugs (rated 9.2 on CVSS) across PHP sessions, PHP-FPM, the core engine, and the date extension.
- Fixed Versions: Upgrade to PHP 8.5.13, PHP 8.4.28, PHP 8.3.37, or PHP 8.2.36.
- The Risk Level: PHP notes that exploiting the critical bugs generally requires non-default settings, shared setups, or specific server conditions rather than a plain default install—but some attack paths are still serious if left unpatched.
- Pro Tip: Don’t rely on `ini_set()` to turn off risky session features at runtime—apply server-level config changes and restart PHP workers cleanly.
PHP Security Release: Seven Critical Flaws Patched Across Supported Versions
The PHP security team rolled out fresh security updates on November 19, 2026, closing 18 vulnerabilities across supported branches—highlighted by seven critical flaws that could allow attackers to crash workers or run unwanted code in certain setups.
If your websites, APIs, or WordPress stacks run on PHP, this is a routine patch window you shouldn’t push off. While PHP notes that the highest-severity flaws depend on specific configurations or server conditions rather than bare-bones defaults, real-world apps often mix settings, plugins, and background jobs in ways that create openings.
What Was Fixed? (The Seven Critical Flaws)
Instead of drowning in heavy memory jargon, here is what the top critical bugs actually mean for a running site:
“`
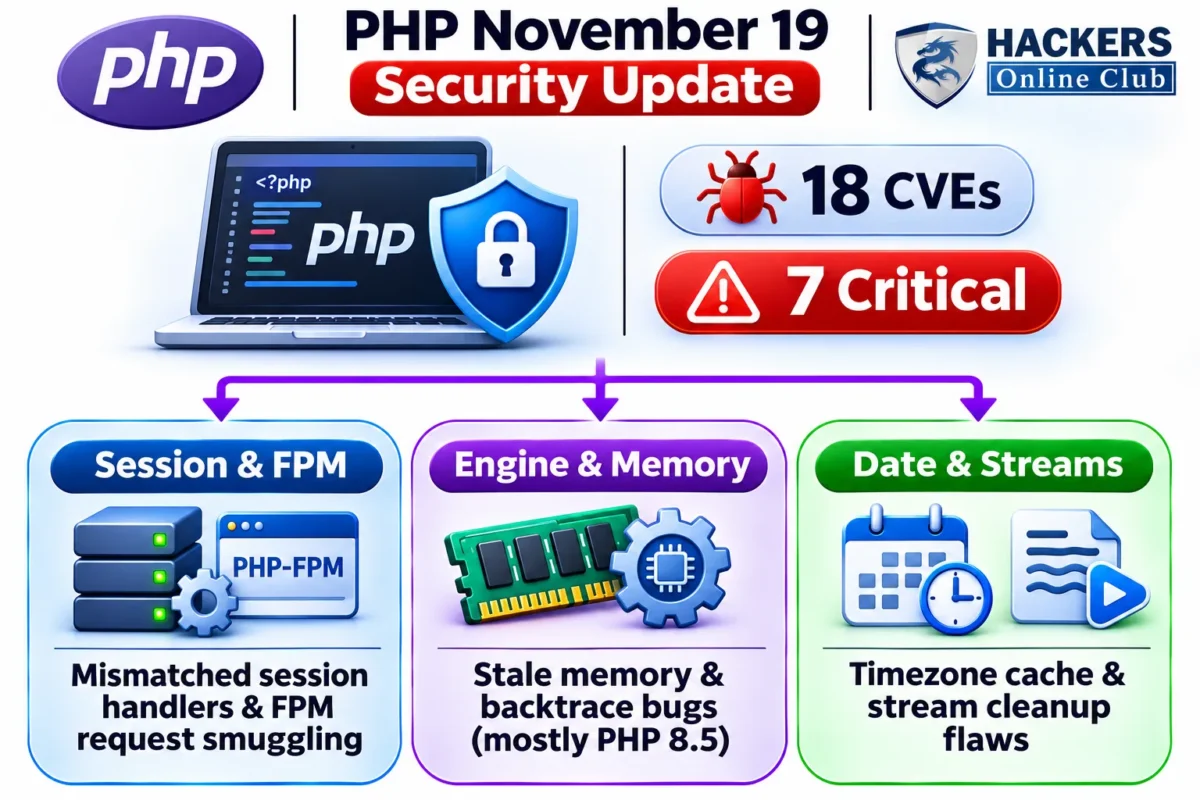
- Session Format Mismatch (`CVE-2026-115560`): Happens when session upload progress is enabled and session data is written in one format but read back in another (such as switching session handlers between `php_binary` or `php_serialize` and `php`), which can lead to severe code execution or data corruption.
- PHP-FPM Request Smuggling (`CVE-2026-129289`): Targets setups where FastCGI connections are reused between requests and request bodies go unread, letting an attacker slip an extra request through.
- Partially Overwritten Session Files (`CVE-2026-126714`): If saving a session gets interrupted mid-way, the session file can end up half-old and half-new, opening doors to abuse if attackers control session data.
- Session Shutdown Memory Bug (`CVE-2026-129481`): Affects PHP 8.3 and newer when a fatal error happens while closing a session stream, leaving memory behind that a later request on the same worker can misuse.
- Magic Method Backtrace Bug (`CVE-2026-129474`): Targets PHP 8.5 setups where function arguments appear in error backtraces and a request hits memory limits at a delicate moment.
- Fatal Error Backtrace Bug (`CVE-2026-129182`): Tied to PHP 8.5 error backtrace handling after shutdown conditions, expanding on prior fixes.
- Timezone Cache Bug (`CVE-2026-129496`): A memory reuse flaw tied to timezone caching when PHP logs startup diagnostics or warnings to its own log file.
(The release also patches 11 other medium- and high-severity bugs across areas like DOM serialization, CGI `PATH_INFO`, Phar signatures, SOAP, and URI parsing.)
Patched Versions at a Glance
| PHP Branch | Fixed Release | Status Note |
| PHP 8.5 | 8.5.13 |
Supported |
| PHP 8.4 | 8.4.28 |
Supported |
| PHP 8.3 | 8.3.37 |
Supported |
| PHP 8.2 | 8.2.36 |
Supported (nearing end of life on Dec 31, 2026) |
Pro Tips for Developers & Site Admins
- Pro Tip 1 — Upgrade First, Don’t Guess Configs: Even if you think your server uses “default” settings, shared hosting, multiple apps sharing a session store, or custom PHP-FPM pools can blur the lines. Move to `8.5.13`, `8.4.28`, `8.3.37`, or `8.2.36` as soon as tested.
- Pro Tip 2 — Set Session Mitigations in `php.ini`, Not `ini_set()`: If you disable `session.upload_progress.enabled` as a stopgap while waiting on a patch window, put it in `php.ini` or your FPM pool config and restart PHP workers—setting it late with `ini_set()` happens too late in the request cycle.
- Pro Tip 3 — Watch Out for Connection Reuse: If you run NGINX or Apache in front of PHP-FPM and use persistent FastCGI connections (`fastcgi_keep_conn` or connection reuse), test your upgrade carefully or turn reuse off temporarily if needed.
- Pro Tip 4 — Plan Ahead for PHP 8.2: If your sites still sit on PHP 8.2, start planning your move to PHP 8.3, 8.4, or 8.5 now so you aren’t scrambling right before year-end.