
HOC Shorts |
What Happened: AI code editor Cursor released an breakdown of the October security incident where fake, modified versions of the popular Claude Code extension (`anthropic.claude-code` versions `2.1.312` and `2.1.313`) sneaked onto their extension marketplace.
- The Root Cause: Hackers didn’t break Cursor’s core security. Instead, they found an exposed cloud service key in an old storage bucket. That key gave them a backdoor into internal developer tools and marketplace publishing systems.
- The Danger: The fake extension was live for about 11 hours on October 29. If installed, it tried to plant a hidden background connection (`svc-telemetry`) on developer laptops.
- The Catch: Simply clicking “uninstall” on the extension is not enough. Affected developers must check their laptops for hidden startup scripts and rotate their login keys immediately.
Cursor Security Incident Update: Stolen Cloud Key and Fake Claude Code Extensions Explained
The code editor Cursor AI has shared a clear, straightforward breakdown of the security incident that rattled developers in late October. If you use Cursor or write code with AI assistance, headlines about software supply chain hacks can feel intimidating.
Below is an easy-to-read guide on what actually happened, how the fake extension got onto computers, and what steps developers need to take to clean up their systems.
How the Hack Happened (Infographic)
Attackers didn’t crack Cursor’s main software defenses. They found an opening through a third-party cloud service:
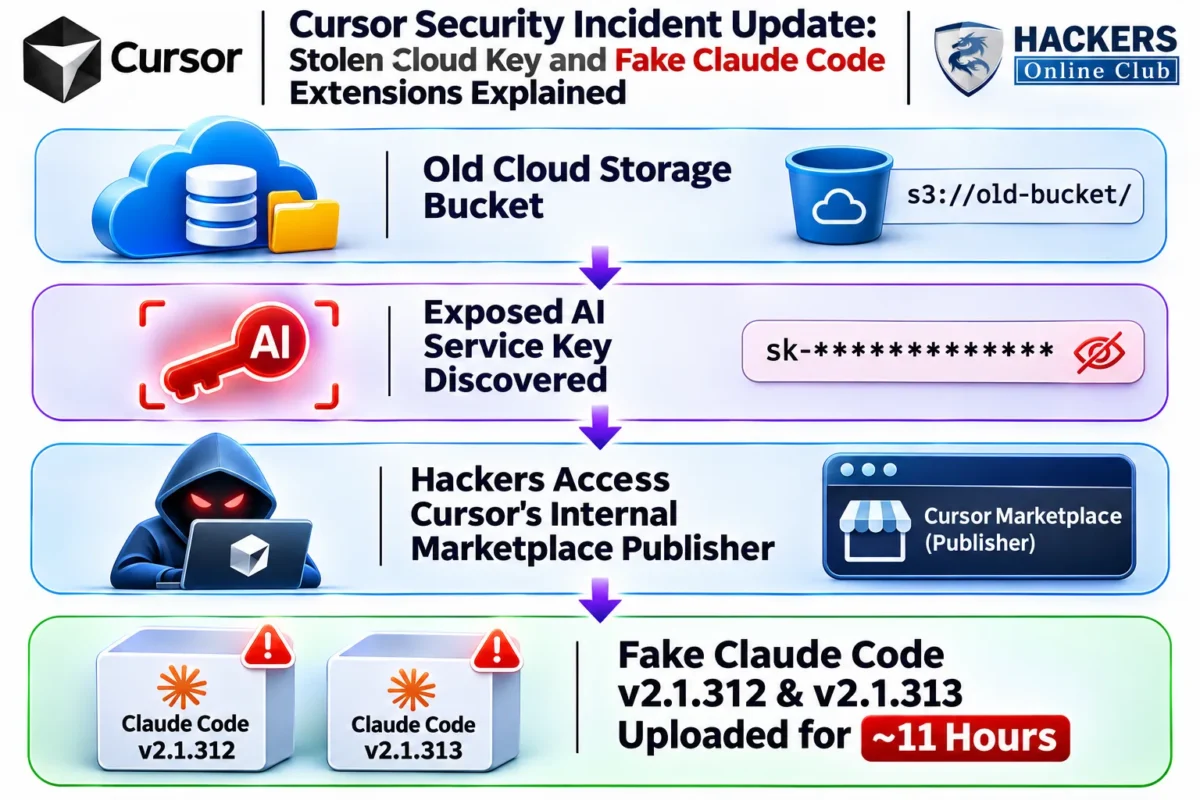
1. The Leaked Key: Hackers stumbled upon an old, exposed cloud key that belonged to a shared AI service platform.
2. The Inside Path: Using that leaked key, the attackers sneaked into Cursor’s internal systems and marketplace publishing dashboard.
3. The Fake Update: On October 29, they pushed modified, malicious versions of the `anthropic.claude-code` extension (`2.1.312` and `2.1.313`) straight to the extension marketplace. The fake update stayed live for about 11 hours before Cursor’s security team caught it and pulled it down.
What Data Was Exposed?
Cursor confirmed that hackers did not access primary customer code repositories or main app servers. However, the attackers managed to look at:
- A few non-production test code repositories.
- Past customer support logs, emails, and AI chat summaries.
- Some API keys that users had previously sent directly to support staff.
What Did the Fake Extension Actually Do?
Security researchers discovered that the modified extension ran a hidden script right when it was installed. Its goal was to set up a secret remote backdoor (`svc-telemetry`) on developer computers to listen for outside commands.
- How It Tried to Hide: On Mac computers, it tried to set up background LaunchAgents; on Linux, cron jobs; and on Windows, automated startup tasks.
- The Good News: Because of system protections and errors on the hacker’s end, active logins failed on most computers.
- The Catch: Because the background scripts were dropped outside the normal extension folder, simply uninstalling the extension from Cursor does not delete the background script.
What Affected Developers Must Do Right Now
If you updated your Claude Code extension around October 29, don’t panic—just take these simple cleanup steps:
1. Check for Unauthorized SSH Keys: Open your terminal and run a quick search to ensure no unknown keys were added to your system:
grep -qs svc-telemetry ~/.ssh/authorized_keys && echo "Key found - Action needed!" || echo "Clean!"
2. Clean Your Startup Scripts: Check your computer’s startup folders, cron jobs, or scheduled tasks to remove any unfamiliar background scripts.
3. Change Your Passwords and API Keys: As a smart safety precaution, rotate any cloud keys, GitHub tokens, or SSH passwords that were saved on that computer during that time.